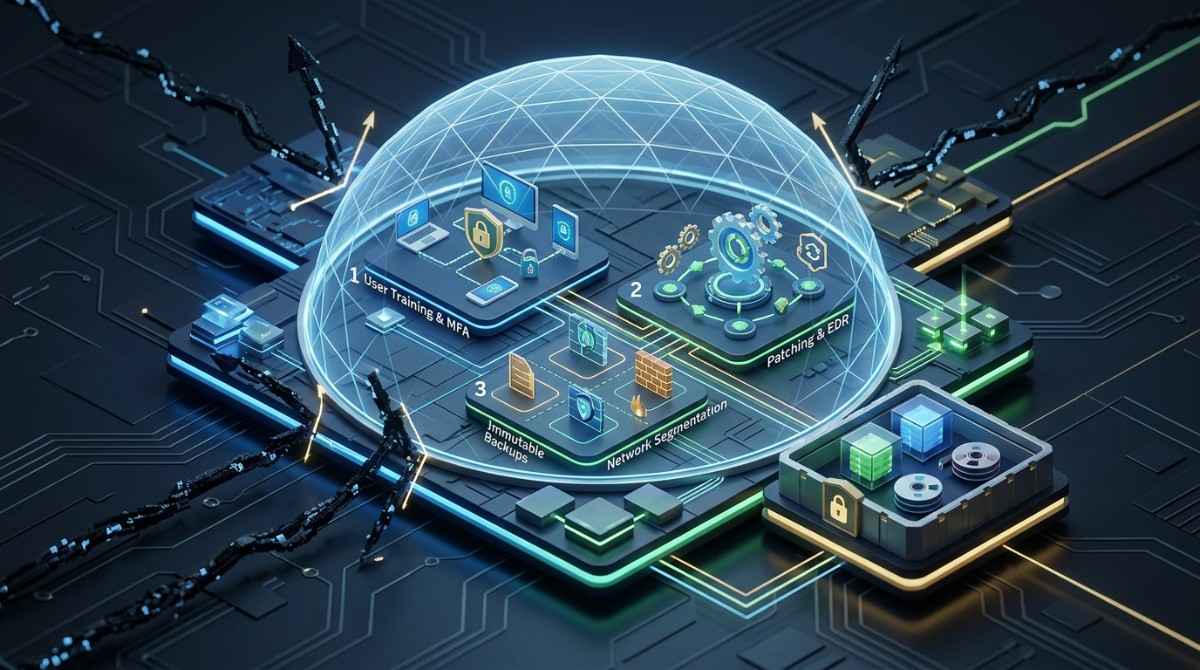
Enterprise Cybersecurity Best Practices to Prevent Ransomware Attacks
Ransomware is no longer a rare headline — it's a routine business risk. Industry trackers reported that global ransomware attacks rose by roughly 20% in the first half of 2026 compared to the same period the year before, with thousands of new victims added to leak sites every quarter. For enterprises, one successful attack can mean days of downtime, regulatory penalties, lost customer trust, and recovery costs that stretch into the millions. The good news is that most ransomware attacks succeed because of preventable gaps — an unpatched server, a weak password, or an employee who clicks the wrong link. This guide walks through practical, easy-to-follow enterprise cybersecurity ransomware prevention strategies your IT team can start applying today.
Why Enterprises Are Prime Targets
Large organizations hold valuable data, run interconnected systems, and can usually afford to pay a ransom — all of which make them attractive to attackers. But size isn't the only factor; complexity is the real problem. The more devices, cloud accounts, remote employees, and third-party vendors an enterprise has, the more entry points exist for attackers to exploit. Recent industry reports even show that small and mid-sized businesses now account for a large share of ransomware victims, because attackers know smaller IT teams often lack the resources of a large security department. In short, no enterprise — regardless of size — can assume it's too small or too obscure to be targeted.
8 Ransomware Prevention Best Practices for Enterprises
1. Build a Security-First Culture Through Employee Training
Most ransomware infections start with a person, not a piece of software — typically through a phishing email or a malicious attachment. Regular, practical security awareness training helps employees recognize suspicious links, spoofed sender addresses, and social engineering attempts before they click. Rather than a once-a-year compliance video, effective programs use short recurring sessions and simulated phishing tests so employees build real habits. Make it easy for staff to report anything suspicious without fear of blame — a quick report can stop an attack before it spreads across the network.
2. Turn On Multi-Factor Authentication (MFA) Everywhere
Passwords alone are not enough to protect enterprise accounts. Multi-factor authentication adds a second verification step — a code, an app prompt, or a biometric scan — so a stolen password isn't enough for an attacker to get in. Enforce MFA across email, VPNs, admin panels, cloud dashboards, and any system holding sensitive data. This single change blocks a large share of account-takeover attempts that would otherwise give ransomware operators a foothold inside your network.
3. Patch and Update Systems Consistently
Attackers frequently exploit known software vulnerabilities that already have a fix available — the organization simply hasn't installed it yet. A structured patch management process covering operating systems, applications, firmware, and network devices closes these gaps before they can be used against you. Prioritize critical, internet-facing systems first, and automate updates wherever possible so patching doesn't depend on someone remembering to do it manually.
4. Segment Your Network and Apply Zero Trust Principles
If ransomware does get in, network segmentation limits how far it can travel. By dividing your network into separate zones — keeping finance systems apart from general employee devices, for example — you contain an infection to a smaller area instead of letting it spread company-wide. Pairing this with a Zero Trust approach, where every user and device must continually verify their identity and permissions rather than being trusted by default, adds another layer that slows attackers down significantly.
5. Maintain Backups That Are Tested and Kept Offline
Backups are your best defense against ever having to pay a ransom, but only if they actually work when you need them. Follow the 3-2-1 rule: keep at least three copies of your data, on two different types of storage, with one copy stored offline or in an immutable format that ransomware can't reach or encrypt. Just as important, test your backups regularly — a backup nobody has ever restored from is a backup you can't rely on during a real crisis.
6. Deploy Endpoint Detection and Response (EDR)
Traditional antivirus software often can't keep up with modern ransomware, which frequently uses new or disguised techniques to slip past basic defenses. Endpoint Detection and Response tools monitor devices continuously, flag unusual behavior — like a program suddenly encrypting large numbers of files — and can automatically isolate an infected device before the damage spreads. Combined with centralized monitoring, EDR gives your security team the visibility needed to catch attacks in their early stages.
7. Manage Third-Party and Vendor Access Carefully
Vendors, contractors, and software integrations often need access to parts of your systems — and attackers know this is frequently the weakest link in enterprise security. Review what access each third party actually needs, remove unused accounts and integrations, and require vendors to meet basic security standards before connecting to your network. A single compromised vendor credential has been the starting point for some of the largest ransomware incidents on record.
8. Build and Practice an Incident Response Plan
Even with strong prevention, no enterprise can guarantee it will never be targeted. Having a written, tested incident response plan — with clear roles, communication steps, and recovery procedures — determines how quickly and cleanly your organization recovers if an attack happens. Run tabletop exercises with your leadership and IT teams so everyone knows exactly what to do in the first hour of an incident, when decisions matter most.
If You Do Get Hit: Think Twice Before Paying
It's tempting to assume paying the ransom is the fastest way back to normal, but the data tells a different story. Organizations that pay are frequently targeted again, since attackers treat a paying victim as a reliable future source of income, while those that recover through backups and a solid response plan are far less likely to be hit a second time. This is one more reason prevention and recovery readiness matter more than negotiation once an attack is already underway.
Final Thoughts
Ransomware prevention isn't a single tool or a one-time project — it's an ongoing combination of trained employees, patched systems, strong access controls, tested backups, and a team that knows what to do when something goes wrong. Enterprises that treat cybersecurity as part of everyday IT operations, rather than an occasional audit item, are the ones that avoid becoming the next headline.
If your business needs help modernizing its security posture — from patch management to building resilient infrastructure — DevLogix's dedicated development teams can help you implement these safeguards without straining your in-house resources. Explore more strategies on our Enterprise IT & Modernization hub, or get in touch with our team to assess where your enterprise currently stands.